Import Your Mixed Evidence Data into The AI Pipeline, And Get a Near-Instant Set of Reports
Investigations are only as strong as the ability to clearly communicate findings. RemiFetch transforms reconstructed timelines, detected behaviors, and correlated activity into structured, comprehensive reports that are grounded in evidence and built for real-world use.
Every finding is directly tied to source data, with clear references, timelines, and supporting artifacts—ensuring transparency, traceability, and confidence in the results. Reports are designed to support investigators, executives, legal teams, and regulators, providing a complete and defensible account of what occurred.
✓
Structured reports combining timelines, findings, and supporting evidence
✓
Evidence-linked findings with direct references to source data
✓
Clear, chronological timelines of events and actions
✓
Attribution of activity across users, systems, and accounts
✓
Exportable, audit-ready reports for legal, compliance, and regulatory use
✓
Complete evidence index with source files and locators
✓
Chain of custody preserved from ingestion through final reporting
AI Generates GPT-Style Reporting And Uses Contextual Data To Produce Narratives
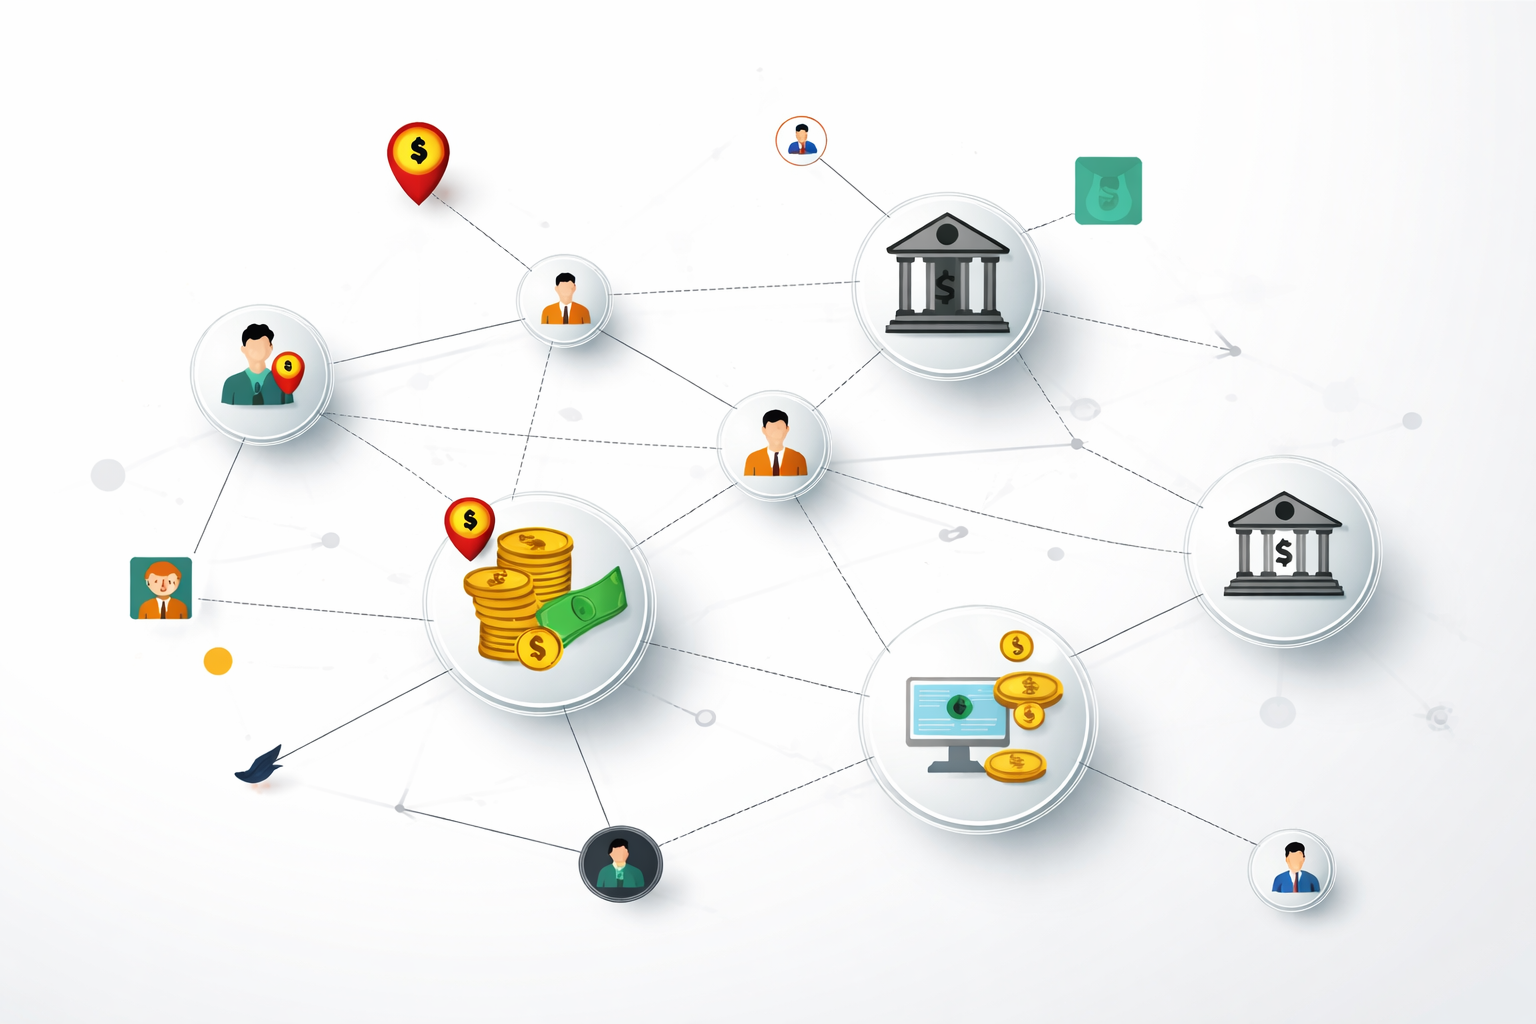
Individual events don’t tell the full story—understanding how they connect is what matters. RemiFetch correlates activity across event logs, systems, accounts, and platforms to reconstruct the complete sequence of an incident.
By aligning events across time and context, correlation reveals how actions relate—connecting user activity, system behavior, and access paths into a single, coherent timeline. This exposes attack progression, links cause and effect, and provides investigators with a clear understanding of what actually happened.
✓
Correlates events across logs, systems, accounts, and platforms
✓
Aligns activity across time to reconstruct a unified incident timeline
✓
Connects user actions, system events, and access paths into one narrative
✓
Reveals relationships between seemingly unrelated events
✓
Maps attack progression from initial access through execution
✓
Identifies cause-and-effect relationships across systems and actions
✓
Produces a complete, evidence-backed timeline for investigation and reporting
What Happened, How Did It Happen, Who Was Involved, What Are The Damages
Correlation is the process of connecting related events across different systems, users, and timelines to understand how an incident actually unfolded. Instead of viewing logs as isolated records, Remi analyzes them together to determine which events are related, who performed them, and how one action led to the next.
AI performs this correlation automatically by examining time proximity, shared attributes, user identities, system interactions, and behavioral patterns. When events share common characteristics—such as the same user account, device, IP address, or command sequence—the AI links them together into a single investigative timeline.
Seeing the Whole Incident Across Systems
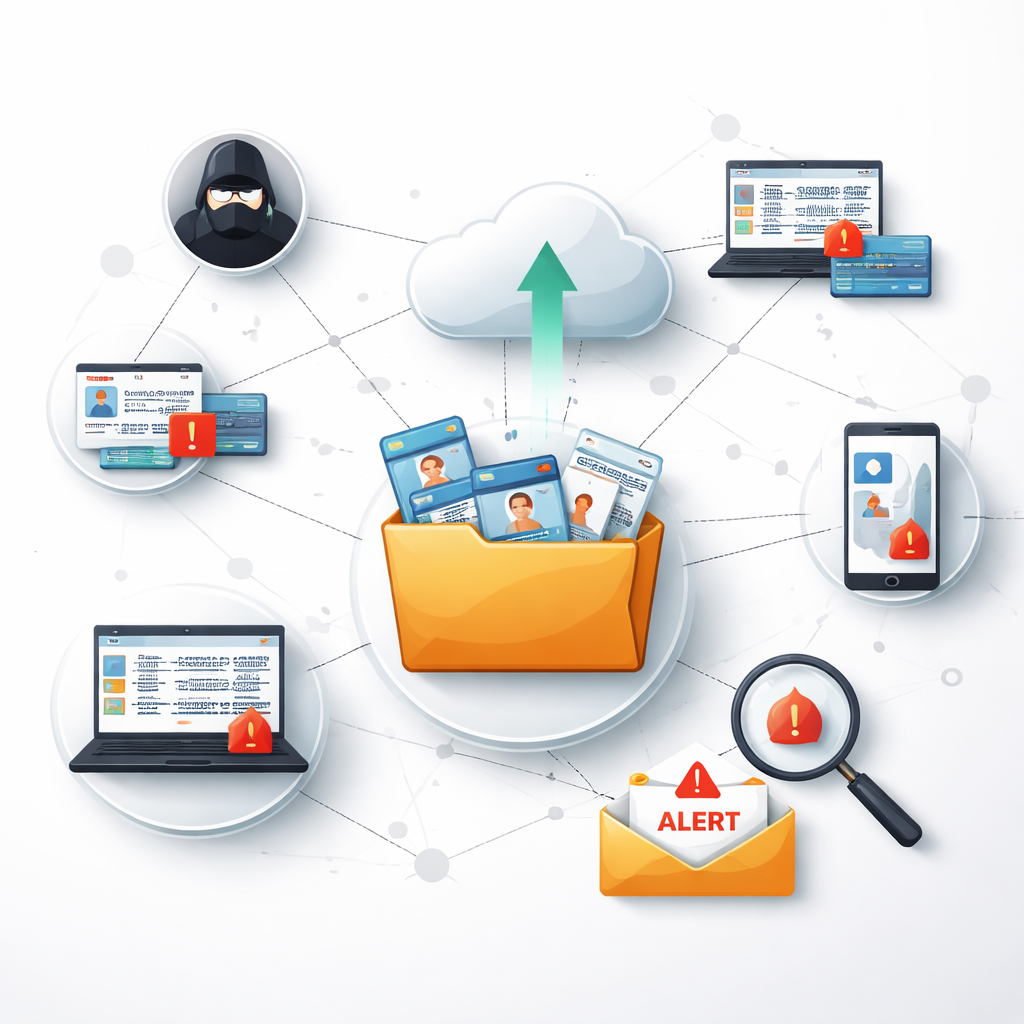
Modern incidents rarely occur on a single system. Activity often moves across multiple devices, platforms, accounts, and services as attackers progress through an environment. Correlation allows Remi to connect these events together so investigators can see the entire landscape of the incident instead of isolated fragments of activity.
The AI analyzes logs and artifacts from different sources—such as workstations, servers, cloud platforms, email systems, authentication services, and network devices—and identifies shared characteristics that link those events together. These connections may include the same user account, IP address, device identifier, file hash, session token, or sequence of actions.
FOR Example
For example, an incident may unfold across several systems:
09:02:11 User login from corporate laptop 09:03:05 Access to internal file server 09:04:18 Sensitive documents downloaded 09:05:02 Connection established to cloud storage account 09:05:27 Documents uploaded to external cloud repository
When these events are correlated across systems, Remi reveals the movement of activity from one platform to another:
Laptop → File Server → Data Download → Cloud Upload
Instead of investigating each system separately, investigators can follow the path of activity as it travels through the environment. This allows them to quickly identify how the incident progressed, what systems were involved, and where the data ultimately went.
By correlating events across devices, platforms, and services, Remi gives investigators a complete operational view of the incident, making it possible to track activity across the entire environment and reconstruct the full chain of events from beginning to end.
AI Identifies Behaviors and Patterns That Reveal the Full Attack
Modern attacks are designed to evade signature-based detection and blend into normal activity. RemiFetch uses AI to analyze event log data and identify behavioral anomalies, repeated actions, and subtle patterns that indicate suspicious or malicious activity.
AI-driven cyber tradecraft has its own distinct patterns—automation artifacts, timing consistency, execution cadence, and non-human interaction sequences. RemiFetch surfaces these indicators directly from event logs, enabling detection of advanced and AI-assisted activity even when no known signatures or rules exist.
✓
Detects behavioral anomalies instead of relying on known signatures
✓
Identifies patterns associated with AI-driven cyber tradecraft
✓
Detects automated or scripted behavior through repetition and timing patterns
✓
Flags abnormal command sequences and system interactions
✓
Surfaces deviations from expected user, system, or process behavior
✓
Highlights non-human interaction patterns and execution cadence
✓
Detects suspicious activity without predefined rules, thresholds, or signatures
Remi Thinks Like an Investigator, and Detects Suspicious Behavior Without Signatures or Deep Packet Inspection
Instead of relying on predefined signatures or known malware indicators, Remi analyzes the characteristics of activity over time. The AI looks at sequences of events, timing patterns, and relationships between actions to determine whether the behavior resembles normal operations or suspicious tradecraft.
For example, a single event by itself may appear normal. But when Remi observes multiple events occurring in a specific sequence or within a short time window, it can identify patterns that indicate automation, coordinated activity, or adversarial behavior.
Examples of How AI Uses Logic, Detections & Patterns to Reconstruct The Events
Individually, each event may appear normal. However, when these actions occur in rapid succession with consistent timing, the behavior begins to resemble automated task execution rather than human interaction.
Remi recognizes this pattern by examining characteristics such as:
• Execution speed — commands occurring faster than typical human interaction • Consistent timing intervals between actions • Repeated command patterns across systems • Logical progression of attacker tradecraft (access → privilege escalation → system modification → concealment)
Rapid Sequential Login Attempts
This pattern may indicate automated credential testing or scripted access attempts, which often occur faster than a human operator could reasonably perform.
User login attempt from workstation A Within 10 seconds → User login attempt from workstation B Within 10 seconds → User login attempt from server console
Detecting AI-Assisted Automated Activity
Individually, each event may appear normal. However, when these actions occur in rapid succession with consistent timing, the behavior begins to resemble automated task execution rather than human interaction.
Remote login to server Within 3 seconds → Command executed to list system accounts Within 2 seconds → Privilege escalation attempt Within 4 seconds → Configuration change initiated Within 2 seconds → Log files cleared
Cross-System Correlation
When events occur across multiple systems within a short timeframe, Remi correlates the activity to identify whether the behavior reflects coordinated operations rather than independent events.
Remote login to engineering workstation Within 20 seconds → Command executed on control system Within 30 seconds → Configuration change on network device
AI doesn’t just analyze evidence—it decides how to analyze it. RemiFetch adapts forensic methodology in real time based on detected patterns, automatically applying the right techniques—correlation, artifact extraction, behavioral analysis, and timeline reconstruction—to match the investigation.
By linking signals across systems and evolving its approach as new evidence emerges, AI reveals relationships and attack paths that static workflows cannot. This enables deeper insight, faster investigations, and defensible, evidence-driven conclusions.
✓
Not dependent on known malware signatures or predefined rules
✓
Detects patterns, behaviors, and relationships across systems and time
✓
Adapts forensic methods dynamically based on the evidence and context
✓
Correlates activity across accounts, devices, networks, and platforms automatically
✓
Identifies multi-stage and coordinated attacks traditional tools often miss
✓
Surfaces hidden relationships and attack paths without manual stitching
✓
Produces evidence-backed findings with defensible, audit-ready timelines
AI That Thinks Like an Investigator
Remi applies artificial intelligence to guide the investigative process itself. Instead of requiring investigators to decide which forensic techniques to run, the AI evaluates the available evidence, identifies investigative leads, and determines which advanced forensic methods should be applied next.
As patterns, anomalies, and relationships emerge, Remi dynamically selects the appropriate analysis techniques—correlating timelines, tracing activity across systems and accounts, and expanding the investigation into related artifacts and behaviors. This allows the system to follow evidence wherever it leads, uncovering connections that traditional tools often miss.
The result is a guided forensic workflow where complex analysis happens automatically. Experienced investigators gain a powerful assistant that accelerates deep analysis, while non-technical users can conduct sophisticated digital forensics without needing to understand the underlying tools, techniques, or data structures.